Security your IT team can sign off on
Who signs in how, who may do what and who changed what when — traceable, operated in Germany and with no US provider in the chain.
In short
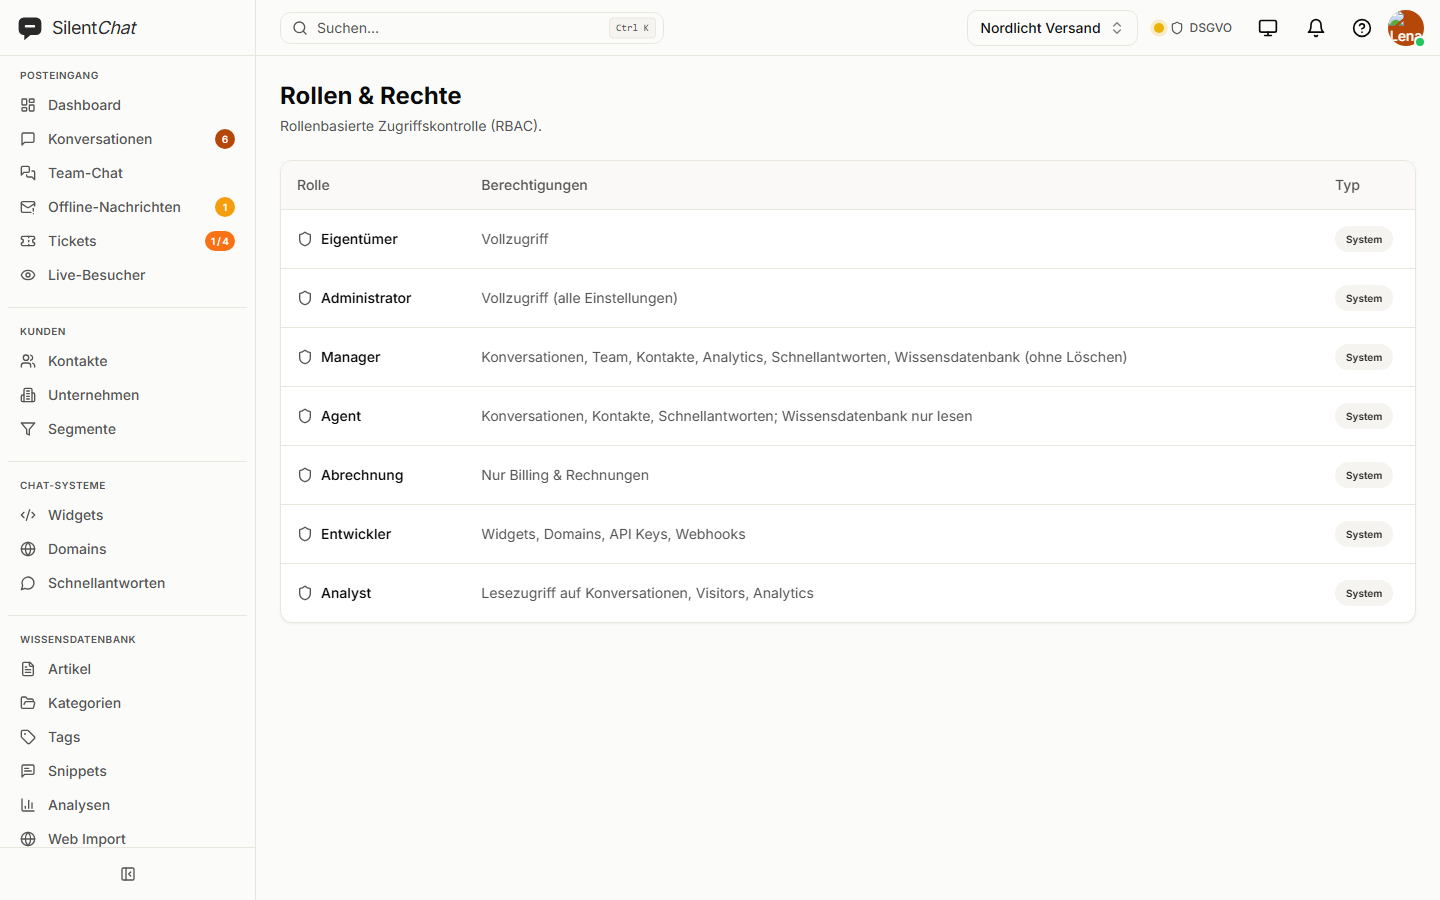
SilentChat secures access to your customer chat with two-factor sign-in for every account and, on the Enterprise plan, single sign-on via SAML. Seven roles with graded permissions govern who may do what; an audit log records who changed what and when. Domain protection prevents your widget from running on other people's sites.
Who may do what — and who did what
Sign in
Password with a second factor, Google or, on Enterprise, your identity provider via SAML.
Permissions per role
From owner to analyst with read-only access — each role sees only its part.
Logged
Security-relevant changes go into the audit log, exportable as CSV or JSON.
What it takes off your team's plate
A second password
With SAML, your people sign in with the account they already have.
Asking “who changed that?”
The audit log names action, time and resource.
Full access for everyone
Accounting sees invoices, the developer sees widgets and keys, the temp sees conversations — nothing more.
Sign-in via SAML
Single sign-on through your SAML 2.0 identity provider, such as Microsoft Entra ID or Okta — with no separate SilentChat password.
Enterprise onlyCustom roles
Fine-tune permissions: 15 areas, each with read, write and delete. Custom roles are currently created via the REST API.
Included from ProfessionalAudit log
Who changed what and when. Retention grows with the plan, and the export delivers CSV or JSON.
Included from StarterDomain protection
The widget loads only on domains you have verified as yours with a DNS record.
Data protection and operations
The application and database run on Hetzner in Germany, the AI on IONOS in Germany, and encrypted backups are stored with Strato in Germany. Chat data is not sent to any US provider.
Data export under Art. 20 GDPR, access and deletion per visitor and retention periods are all settings you manage yourself in the dashboard.
Read more in: Security · Technical and organisational measures · Sub-processors
Frequently asked questions
Yes, on the Enterprise plan. Your people sign in through your identity provider, with no separate SilentChat password.
Yes, for every account and on every plan: with an authenticator app that generates one-time codes.
Seven system roles: owner, administrator, manager, agent, billing, developer and analyst. Custom roles with permissions per area are created via the REST API.
That depends on the plan — from 30 days to two years. You can export it at any time as CSV or JSON.
In Germany: application and database on Hetzner, the AI on IONOS, encrypted backups with Strato. The full list is on the sub-processors page.
Goes well with
Last updated: 23 September 2026
Show your data protection officer the facts
Everything about operations, sub-processors and measures is on one page.